Business email compromise schemes bypass perimeter defenses not by breaking cryptographic protocols, but by exploiting cognitive routines within corporate accounts payable workflows. In mid-2022, an un-named Iowa firm transferred over $800,000 to an unauthorized account under the assumption that it was satisfying genuine vendor liabilities. Four years later, federal forfeiture actions recovered approximately $375,000. This case offers a structural window into the friction, latency, and capital loss inherent in modern wire diversion recovery operations.
The Vector Mechanics of Payment Interception
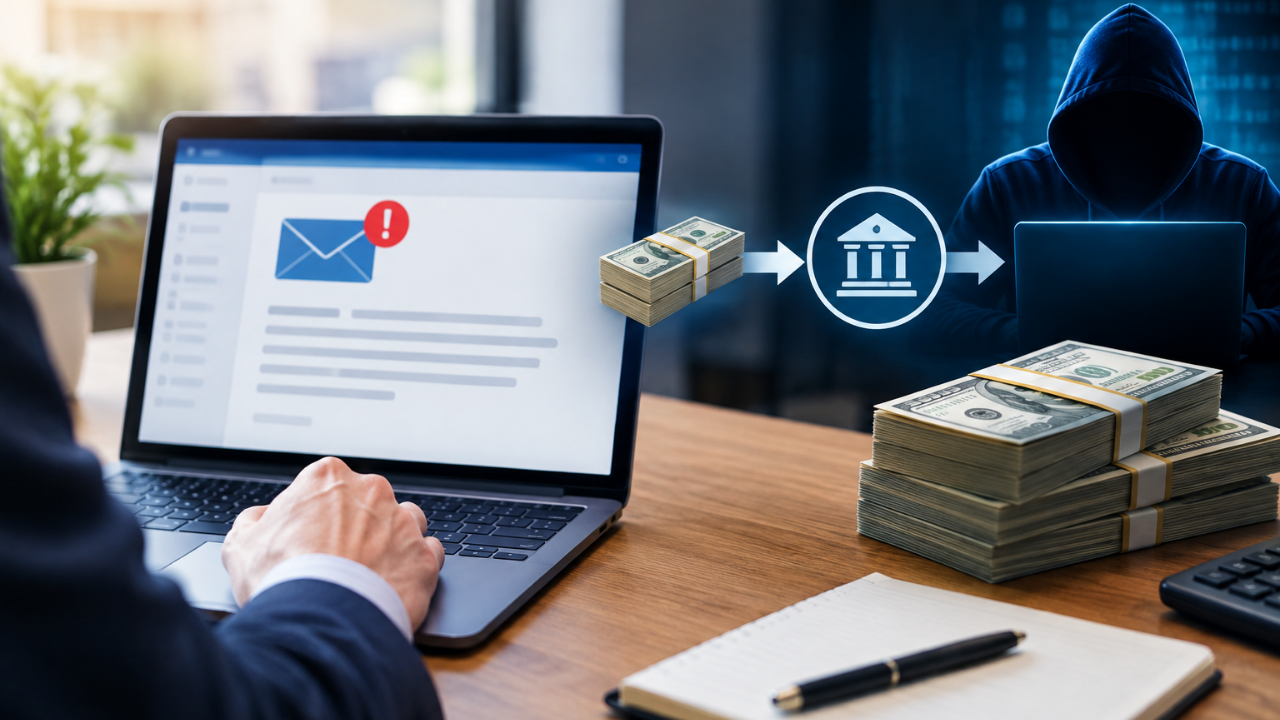
Traditional cyberattacks focus on network intrusion or malware deployment. Business email compromise relies instead on social engineering embedded within routine operational channels. The attack vector requires three minimal conditions:
- Compromise or spoofing of a communication node within the vendor-client correspondence chain.
- Identification of an active billing cycle with an upcoming disbursement.
- Insertion of modified routing instructions that mirror established corporate formatting.
The operational risk escalates because the transaction utilizes existing organizational approvals. The invoice corresponds to a real service or good, the internal employee possesses the authorization to pay, and the disbursement matches expected expenditure baselines. The intervention point occurs solely at the metadata level: the routing number and account identifier are substituted just prior to execution. Consequently, automated bank fraud detection systems frequently fail to flag the transfer because the transaction profile matches historical payment behavior to a known vendor category.
The Cost Function of Capital Recovery
Recovery following a successful business email compromise is constrained by institutional latency and the velocity of transnational fund movement. When capital enters an unauthorized account, the automated clearing house or wire network treats the instruction as valid. Reversing the transaction requires human intervention across multiple jurisdictions, correspondent banks, and law enforcement agencies.
The timeline observed in the Iowa proceeding highlights the structural gap between capital loss and legal resolution:
- Minute Zero: The wire transfer executes, moving capital from the victim's commercial account to the intermediary destination.
- Day One to Week One: Discovery of the discrepancy, internal notification, and reporting to the Federal Bureau of Investigation via the Internet Crime Complaint Center.
- Month One to Year Four: Financial tracking, subpoena issuance, asset freezing, and civil or criminal forfeiture proceedings to secure specific accounts holding traceable proceeds.
In this instance, investigators successfully traced and froze $372,583.77 within a specific Wells Fargo holding account. A federal court entered a forfeiture judgment four years later. The delta between the original $800,000 outflow and the recovered sum illustrates that once funds disperse through multi-tiered laundering networks—frequently transformed into alternative financial instruments or cross-border transfers—complete recovery approaches zero probability.
The Dual Obligation Dilemma
A structural oversight in post-fraud analysis is the failure to account for dual liabilities. When a commercial entity transfers funds to an impostor, two distinct financial obligations remain active:
- The loss of working capital resulting from the fraudulent diversion of funds.
- The unresolved commercial debt owed to the legitimate vendor whose invoice was intercepted.
Because the initial payment was directed to an unauthorized entity, the legal liability to the actual vendor is generally unfulfilled. The enterprise faces an immediate liquidity shock: capital has exited the balance sheet, yet the underlying operational obligation persists. Insurance recovery, where applicable, involves extended adjustment periods, proof of loss evaluations, and friction regarding policy exclusions related to voluntary wire instructions.
Institutional Controls Versus Operational Friction
Organizations typically respond to payment diversion events by implementing binary access controls. However, security measures introduce operational friction that can impair supply chain velocity. Effective risk mitigation requires distributing controls across orthogonal verification channels rather than relying on single points of failure.
- Out-of-Band Verification: Mandating that any modification to banking instructions, routing numbers, or beneficiary titles triggers a verification protocol via a pre-established, independent communication channel never sourced from the incoming invoice email.
- Segregation of Ingestion and Execution: Ensuring that personnel who update master vendor data files do not possess the authorization to execute wire disbursements.
- Velocity Thresholds: Establishing mandatory holding periods or dual-authorization requirements for non-standard disbursement modifications exceeding specified capital limits.
The recovery of partial proceeds via federal forfeiture demonstrates that investigative mechanisms function when assets remain stationary within domestic institutions. However, reliance on judicial asset recovery as a primary defense strategy represents a fundamental misallocation of capital protection resources. Prevention architecture must be designed around the assumption that once a wire leaves the originating ledger, recovery is an exception rather than a remedy.